We set up the SOC in Slovakia in 2014 based on our experience from challenging projects involving the protection of major European Union institutions, corporate IT security, intelligence agencies, ethical hacking and cybercrime investigations. Our services are used by large multinational companies as well as organisations with specific and clearly-defined needs.
And with our commitment to continuous development, we are rightly referred to as the quality leader in Slovakia in terms of SOC as a Service.
Understandable and clear reports for the management
Expert Team
Certified and highly professional security team
PREVENTION
Vulnerability monitoring and management
[how our soc works]
A high-quality SOC involves a complex field where success directly depends on a well-chosen strategy, implemented technology, properly set up processes and, most importantly, the skills of the monitoring centre staff.
Binary Confidence SOC is a managed service that combines automated analysis and human intelligence to detect security breaches. Logs and events are collected from client’s devices and are subsequently encrypted and transmitted for a two-level analysis in the Security Operations Centre.
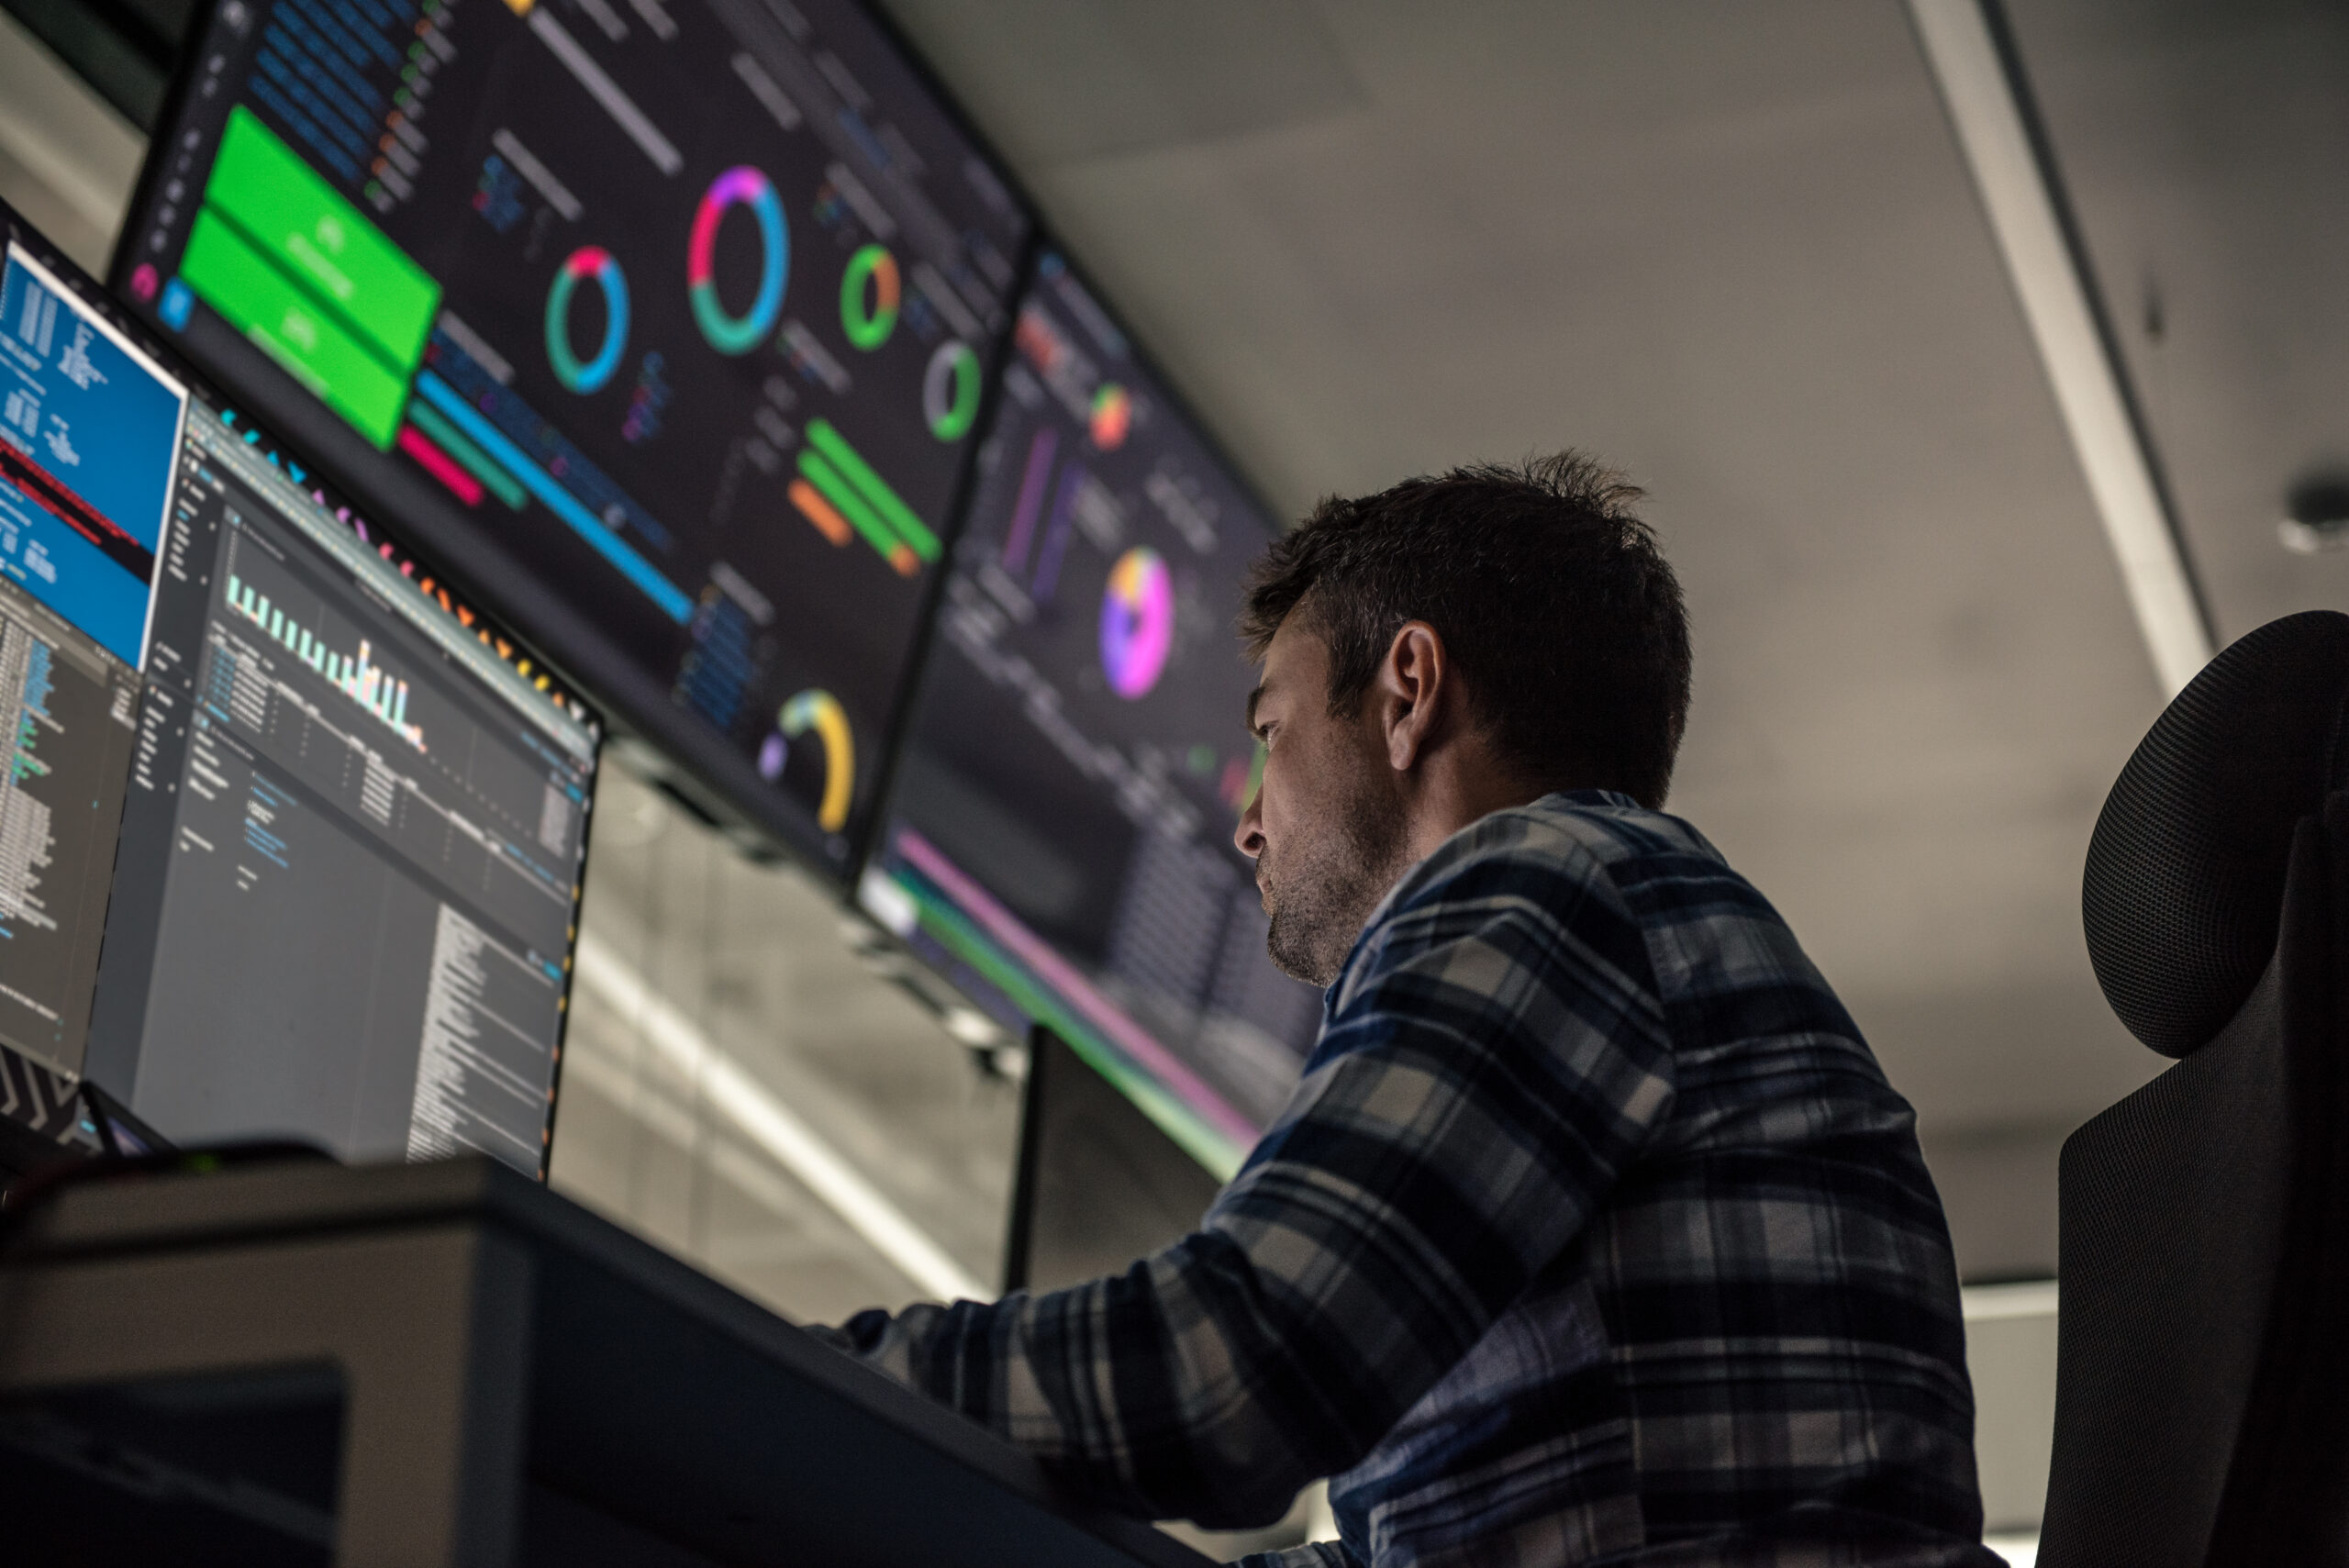
Watching a security team at work says more than any technical description. In this video, our SOC analysts detect, investigate and handle a simulated cyberattack in real time.
Jan pôsobí ako SOC Manager a zodpovedá za riadenie dohľadového centra kyberbezpečnosti (SOC) a bezpečnostnych operácii.
Svoju kariéru začal v oblasti fyzickej bezpečnosti v Londýne, kde viac ako 10 rokov viedol projekty zamerané na implementáciu systémov access control, CCTV a intrusion detection pre rozsiahle objekty. Táto skúsenosť ho prirodzene nasmerovala do kyberbezpečnosti. Následne pôsobil aj ako bezpečnostný analytik a dnes vedie SOC tím, pričom využíva praktické skúsenosti s detekciou a riešením incidentov.
Má viac ako päť rokov skúseností v Security Operations a, mimo iných technických, je i držiteľom prestížnej certifikácie SANS GSOM.
Ján is a co-founder of Binary Confidence and a network expert specialising in IT systems and network security. He graduated from the University of Žilina in the study field “Information and Security Systems” and has over 14 years of experience in detecting and responding to incidents.
He has also participated in an exercise organised by the NATO Cyber Defence Centre of Excellence where he ranked in the highest percentile in his group.
The SOC Binary Confidence team is composed of experts with many years of experience in IT and information security, specialising primarily in SOC and solving cybersecurity problems in areas such as Threat Hunting, Cryptography, Forensic Analysis and Incident Management. They possess high-level knowledge and skills in new technologies such as SIEM, SOAR and many others.
Consistent education constitutes an integral part of SOC analysts’ daily work routine. Attending professional conferences, sharing best practices within the team on a daily basis, obtaining certifications.
The SOC Binary Confidence team has the following certifications.:
C|EH, E|CIH, CCDCOE, CISSP, CISM, CSA, CHFI, SECURITY+, Accredited by TI
In order to provide TOP quality services, we have set up a structure with clearly defined qualifications and roles within the SOC. The SOC Binary Confidence team is composed of SOC Manager, SOC Deputy Manager, Level One SOC Analysts, Level Two SOC Analysts, as well as specialists in forensic analysis and cooperation with the law enforcement bodies. These services are provided 24/7.